Documentation / Guides
Authentication
All /v1 endpoints (except /v1/oauth/token itself) require a bearer access token.
Get one via the client_credentials grant:
POST /v1/oauth/token
{ "client_id": "...", "client_secret": "..." }
This returns a token valid for 1 hour, carrying the scopes your application was approved
for. Pass it as Authorization: Bearer <token> on every request.
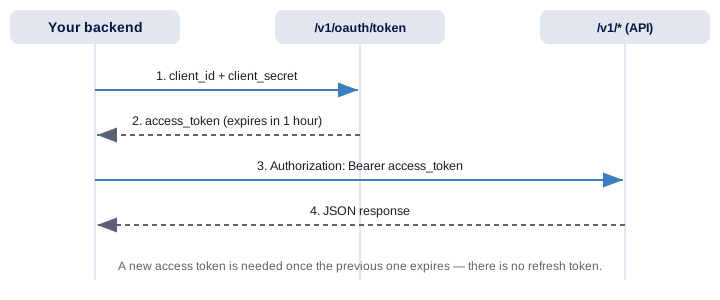
There's no refresh token — once it expires, request a new one the same way.